California public agencies and the vendors serving them are increasingly required to demonstrate automated, auditable incident response capability, not just a written policy sitting in a binder, as a condition of funding and compliance for state cybersecurity programs. For businesses in this ecosystem, whether a direct state contractor, a local government IT vendor, or a company processing data on behalf of a California public entity, understanding what automated incident response actually requires, and where funding intersects with that requirement, is now a practical operational question, not a theoretical one.
In short. California public agencies and the vendors that serve them increasingly need to show automated, auditable incident response, not just a written policy, to meet state cybersecurity funding and compliance expectations. In practice that means a detection-to-documentation workflow that alerts the right people, logs every action with timestamps and produces the evidence an auditor asks for.
Why This Matters Beyond Direct State Agencies
California's cybersecurity funding and compliance framework has ripple effects well past the agencies themselves. Vendors and contractors serving state and local government are frequently required to meet comparable incident response standards as a condition of the contract, and businesses handling California resident data more broadly face incident response expectations under state privacy law regardless of whether they contract directly with government.
What "Automated Incident Response" Actually Means Here
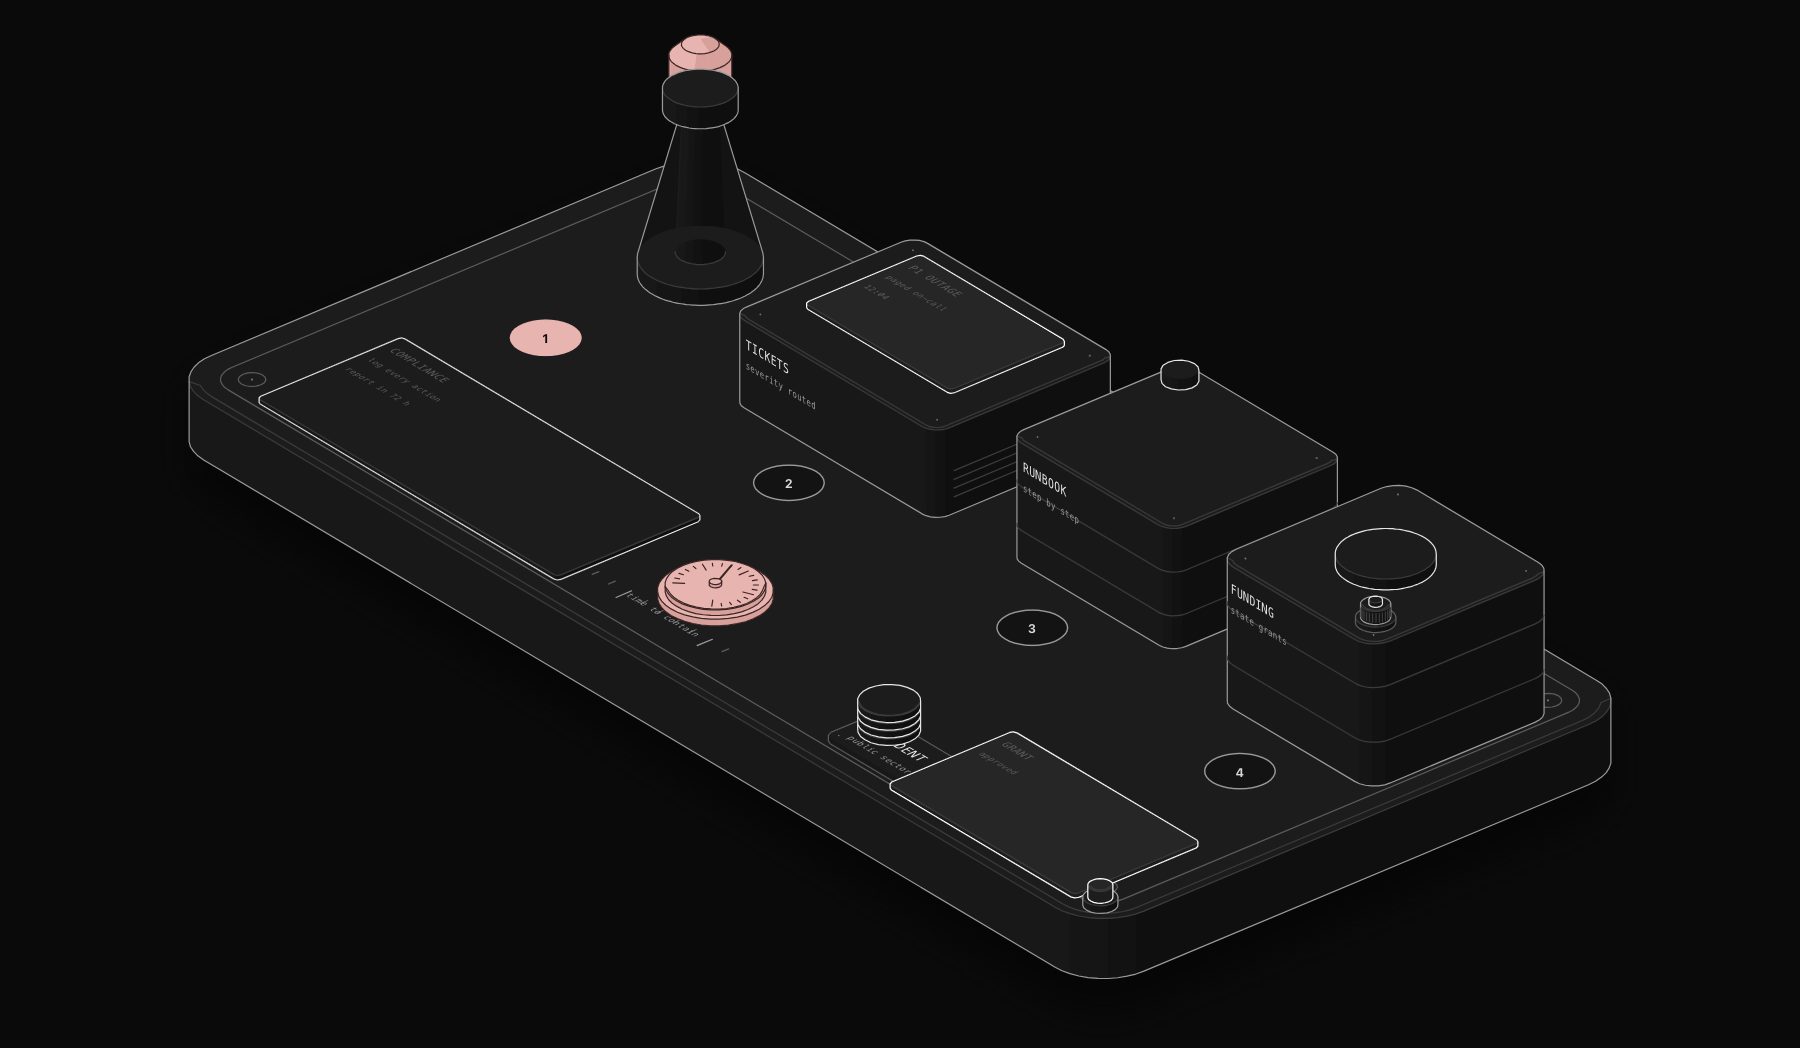
This is not a single product purchase. It is a workflow: detection (a security event is flagged), triage (the event is classified by severity and type), notification (the right people and, where legally required, the right regulatory bodies are notified within mandated timeframes), and documentation (a complete, timestamped audit trail exists for the entire response).
The automation layer is what makes the notification timing and audit trail reliable. Manual incident response, where a person has to remember to escalate, notify, and document under pressure during an active incident, is exactly where compliance failures happen, not because anyone acted in bad faith, but because manual processes break down when they matter most.
The Automation Workflow
- Detection layer: security monitoring tools (SIEM, endpoint detection) generate the initial signal, whether that is a technical tool or a reported event from a staff member.
- Triage layer: an automated workflow classifies the event by severity and type against a predefined framework, rather than waiting for a person to manually assess it under time pressure.
- Notification layer: based on classification, the workflow automatically notifies the appropriate internal stakeholders and, where a mandated timeframe applies, prepares the required external notification with the specific details regulations require.
- Documentation layer: every step, timestamp, and decision gets logged automatically, producing the audit trail that funding and compliance reviews actually look for, rather than requiring someone to reconstruct a timeline after the fact from memory and scattered emails.
Why This Is Genuinely Different From General IT Automation
Incident response automation has to handle the case where the very systems the workflow depends on may themselves be compromised or degraded during an active incident. This means the notification and logging layer needs redundancy that a typical business automation workflow does not require, since it may need to function even when parts of the primary infrastructure are the thing under attack.
Getting Started
Businesses in this position typically start with a gap assessment: what does the current incident response process actually do today, manually, versus what a funding or compliance review will expect to see demonstrated. This is the same audit-first principle behind every automation deployment we run, detailed in our workflow automation consulting guide, applied here to a compliance-critical rather than purely operational workflow.
The Detection-to-Documentation Chain
| Stage | What automation handles | What stays human |
|---|---|---|
| Detection | Automated monitoring flags anomalies against defined thresholds | Initial triage of whether a flagged anomaly is a genuine incident |
| Notification | Automated alerts to the defined response team within the required timeframe | Deciding severity classification and which stakeholders beyond the core team need notification |
| Documentation | Automated logging of every action taken, with timestamps, for the compliance record | Writing the narrative incident report required for regulatory submission |
| Remediation tracking | Automated reminders and status tracking against remediation deadlines | Actually performing and verifying the remediation work itself |
Funding and compliance requirements in this space typically focus on the detection and documentation stages specifically, since those are the ones auditors can verify objectively (did the alert fire within the required window, does the documentation trail exist and match the required format), which is exactly why they're also the highest-leverage stages to automate rather than handle manually under incident pressure.
Frequently Asked Questions
Is automated incident response a strict legal requirement, or a funding condition?
It varies by context. Some requirements come from specific state cybersecurity program conditions tied to funding or contracts, while others stem from broader California privacy law obligations around timely breach notification that apply regardless of funding relationships. The specific requirement depends on your organization's relationship to state and local government and the type of data involved, and should be confirmed against current program guidance rather than assumed.
Can a small vendor realistically build this without a large security team?
Yes, with the right scope. The workflow layer, classification, notification, and documentation, can be built on existing security tooling without requiring an in-house security operations center, particularly when a workflow automation layer handles the coordination and audit trail rather than requiring manual process discipline under pressure.
What is the biggest gap most organizations have in current incident response?
Documentation and timing. Detection tools are common; automated, timestamped documentation proving notification happened within a required window is the piece most manual processes fail to produce reliably, precisely because it depends on someone remembering to log it accurately during an active, stressful incident.
Does this replace the need for a written incident response policy?
No. The written policy defines what should happen and who is accountable. The automation is what makes that policy actually executable and auditable under pressure, rather than a document that describes an ideal that manual process cannot reliably deliver during a real incident.
How long does it take to build an automated incident response workflow?
A workflow covering detection-to-notification automation for a defined set of incident types typically takes 2 to 4 weeks to build and test against tabletop exercise scenarios before being considered production-ready, depending on the number of systems and notification requirements involved.
Tags
Purist Team
The PURIST editorial team covers automation, AI agents, and operations strategy for businesses scaling with n8n, Make, and Claude AI.